X.509 Certificates

X.509 Certificates

X.509 certificates provide the most secure authentication method for IoT devices on /IOTCONNECT™. They enable mutual TLS authentication where both the device and the platform verify each other’s identity using cryptographic certificates, ensuring only trusted devices can communicate with your IoT infrastructure.

What Are X.509 Certificates?

X.509 is an international standard (ITU-T) that defines the format of public key certificates. In the context of IoT, X.509 certificates bind a device’s identity to a public key, allowing the platform to verify authenticity without transmitting secrets over the network.

Each X.509 certificate contains:

Subject: The identity of the certificate holder (typically the device common name or unique ID).

Public Key: The device’s public key used for encryption and verification.

Issuer: The Certificate Authority (CA) that signed and issued this certificate.

Validity Period: The start and expiration dates defining when the certificate is valid.

Signature: The digital signature from the issuing CA proving the certificate is authentic.
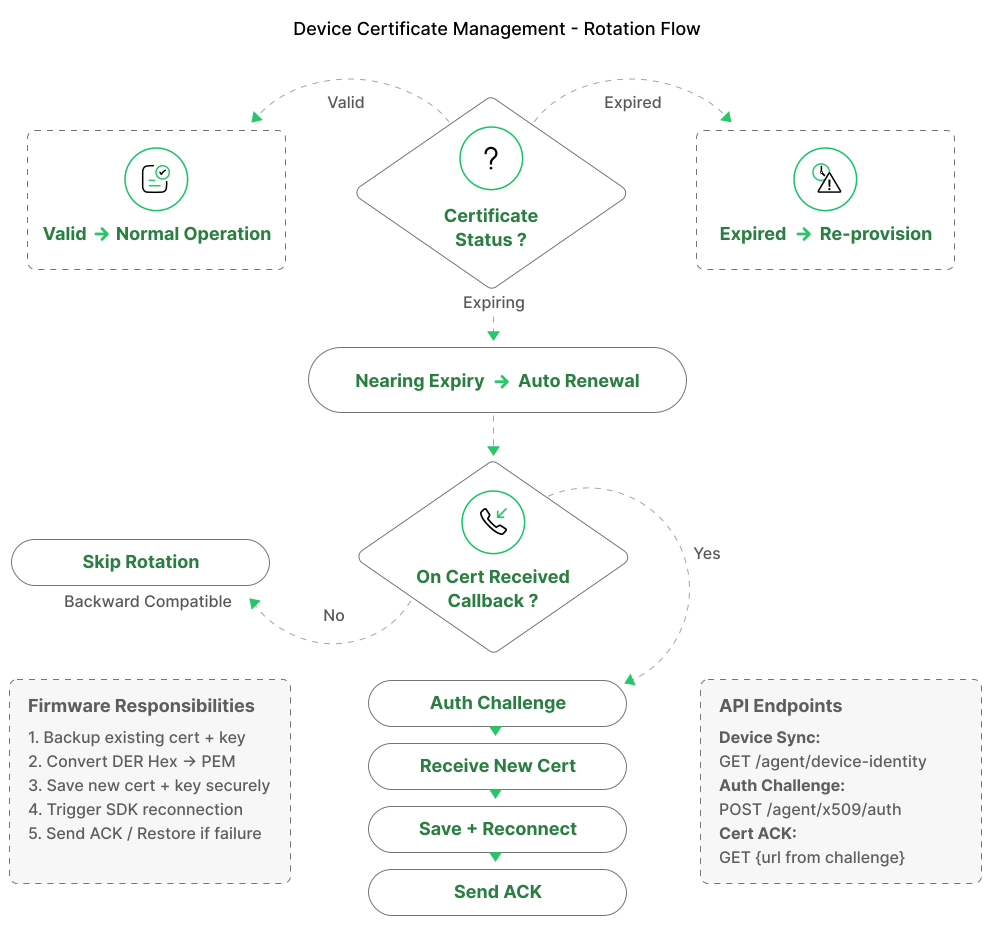
How X.509 Works with IoT Devices

When a device with an X.509 certificate connects to /IOTCONNECT™, the following authentication flow occurs:

1. The device initiates a TLS connection to the platform endpoint.

2. The platform presents its server certificate (device verifies it’s connecting to the real platform).

3. The device presents its client certificate to the platform.

4. The platform validates the device certificate against registered CA certificates.

5. The platform extracts the device identity from the certificate’s Common Name (CN) field.

6. Upon successful validation, a secure mTLS channel is established.

This process ensures that no shared secrets are transmitted over the network, and device credentials cannot be intercepted or replayed.

CA-Signed vs Self-Signed Certificates

/IOTCONNECT™ supports both CA-signed and self-signed certificates for device authentication:

CA-Signed Certificates (Recommended for Production)

CA-signed certificates are issued by a Certificate Authority that you register in the /IOTCONNECT™ portal. Any device presenting a certificate signed by this CA is automatically trusted. This approach enables zero-touch provisioning at scale — new devices are authenticated without manual registration of each certificate.

Self-Signed Certificates

Self-signed certificates are generated and signed by the device itself (or by your own tooling) without a CA hierarchy. These must be individually registered in /IOTCONNECT™ for each device. Self-signed certificates are suitable for development, testing, and small deployments where managing individual certificates is feasible.

Certificate Chain of Trust

The chain of trust works as follows:

Root CA → Device Certificate: Simple two-level hierarchy. The Root CA directly signs device certificates. Best for smaller deployments.

Root CA → Intermediate CA → Device Certificate: Three-level hierarchy. The Root CA signs an Intermediate CA, which then signs device certificates. Recommended for production — the root key stays offline and protected.

Creating a CA Certificate in the Portal

Prerequisites

CA Certificate File: A PEM-encoded (.pem) Root CA or Intermediate CA certificate file ready for upload.

Portal Access: Admin or appropriate role access to the /IOTCONNECT™ portal Security section.

OpenSSL (Optional): For generating verification certificates during the proof-of-possession step.

Steps to Create a CA Certificate

Step 1: Navigate to the Security section in the /IOTCONNECT™ portal and select Certificates.

Step 2: Click Create Certificate to open the certificate creation form.

Step 3: Enter a descriptive Certificate Name (e.g., “Production-RootCA-2024”).

Step 4: Upload your CA certificate file (.pem format).

Step 5: The portal generates a Verification Code. Use this code to create a verification certificate signed by your CA private key.

Step 6: Upload the verification certificate to complete proof-of-possession. This proves you own the CA private key.

Step 7: Once verified, the certificate status changes to Verified and devices signed by this CA can authenticate.

Certificate List Management

The /IOTCONNECT™ portal provides a certificate list view where you can manage all registered CA certificates. The list displays the following information:

Certificate Name: The descriptive name assigned during creation.

Origin: Whether the certificate was created in the portal or imported externally.

Status: Current state — Pending Verification, Verified, or Expired.

Expiry Date: When the certificate expires and needs rotation.

Reference ID: Unique identifier for API and enrollment group references.

From the certificate list, you can verify pending certificates, view certificate details, rotate expiring certificates, and delete certificates that are no longer needed.

ⓘ NOTE

The device certificate’s Common Name (CN) must match the device’s unique ID registered in /IOTCONNECT™. If the CN does not match, the device will fail authentication even if the certificate chain is valid.